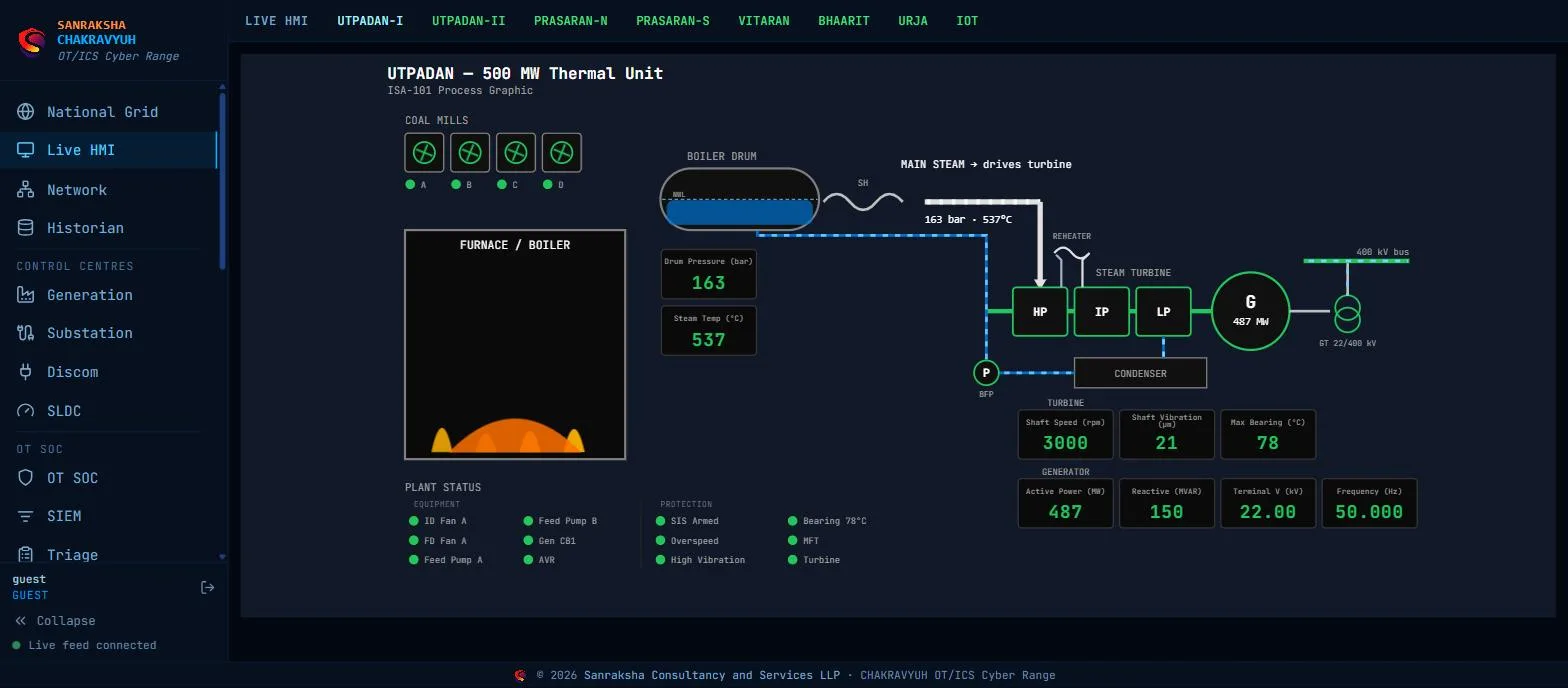
Register-level PLC maps
Coils, discrete inputs, holding and input registers per sector, with protection relays (87G, 40G, distance zones) and turbine, boiler and generator instrumentation.
Sanraksha.CHAKRAVYUH · OT · ICS · SCADA CYBER RANGE
Sanraksha.CHAKRAVYUH is a production-grade OT/ICS cyber range. It simulates power generation, transmission, distribution and refineries down to the PLC register level, drives them with real process physics, and lets you attack and defend them from a live OT SOC.
01 · SIMULATE
Every sector is a live Modbus/DNP3 device map modelled on real Indian infrastructure: a 500 MW thermal unit, a 400 kV substation, distribution feeders and a refinery crude unit, with realistic dynamics, measurement noise and 2-of-3 safety voting.
Coils, discrete inputs, holding and input registers per sector, with protection relays (87G, 40G, distance zones) and turbine, boiler and generator instrumentation.
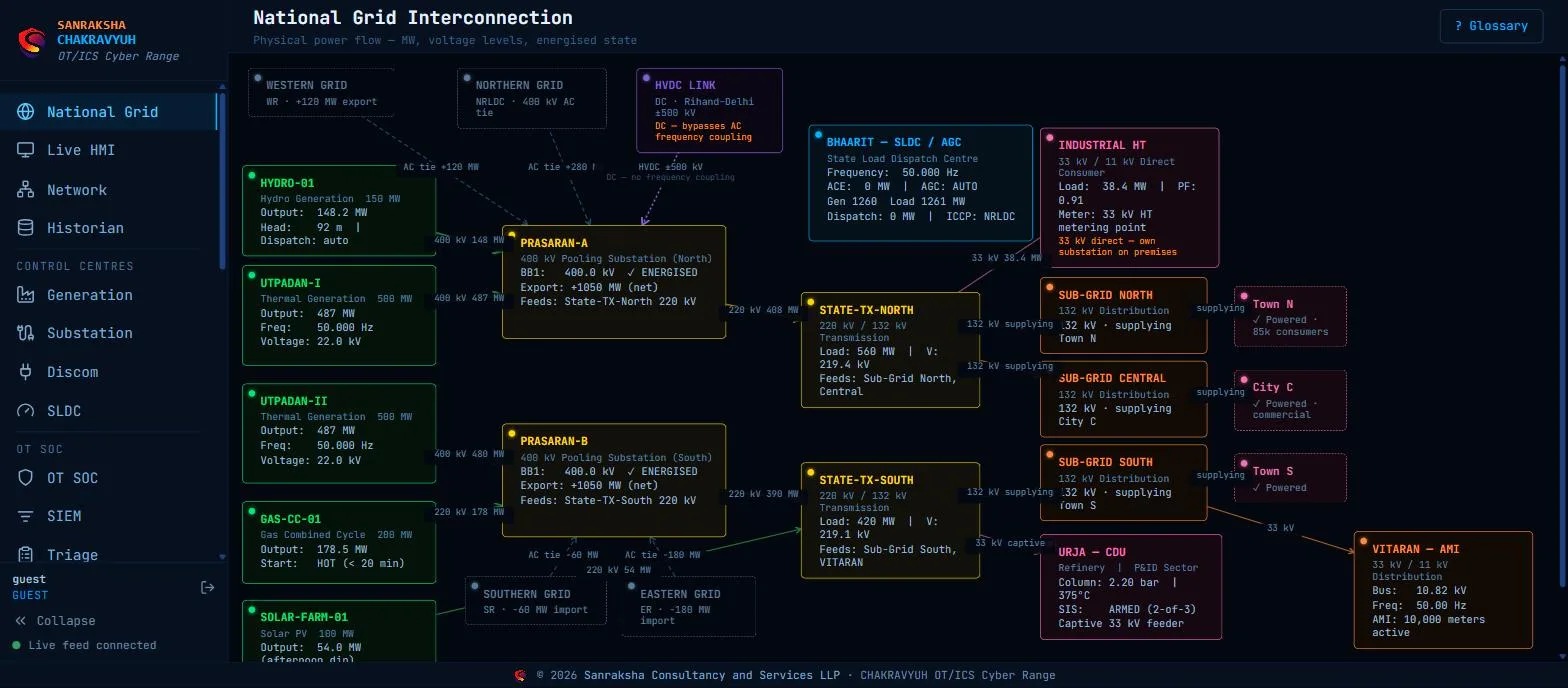
First-order lag dynamics, grid inertia, AGC control loops and SIS voting. Push a setpoint and the plant responds the way a real unit would, with alarms and trips.
ISA-101 process mimics, substation single-line diagrams and refinery P&IDs, plus a full historian with tag browser, multi-pen trends and alarm history.
02 · DETECT
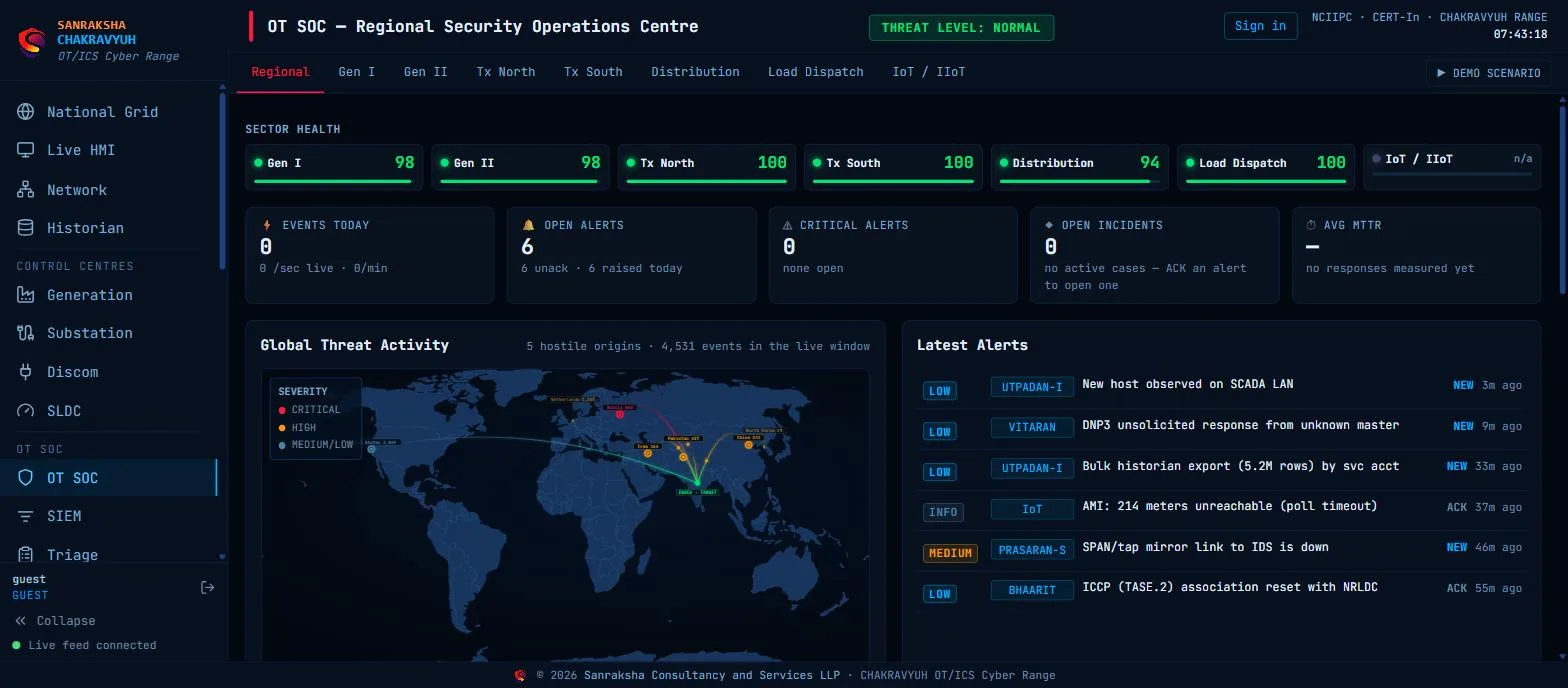
Work a live alert stream fed by Zeek OT protocol analysers and Suricata, mapped to the Purdue model and MITRE ATT&CK for ICS: which sector is under attack, which technique is running, and what to do about it.
Modbus writes, illegal function codes, rapid polling, GOOSE anomalies and RDP pivots surface as prioritised alerts with the Purdue level and kill-chain stage.
Passive and active discovery builds the OT asset inventory by Purdue level, with protocols, firmware versions and the detections watching each device.
An LSTM autoencoder learns normal process behaviour and flags deviations a signature never would, alongside an always-on statistical z-score detector.
03 · ATTACK
Twenty-plus scenarios modelled on real ICS incidents (CRASHOVERRIDE, TRITON, Stuxnet-style logic changes, cascade failures, protection miscoordination), each animating its effect on the live HMI so defenders see the damage as it happens.
CRASHOVERRIDE, TRITON/SIS bypass, historian pivots, GOOSE spoofing, AGC hijack and rogue RTU injection, staged phase by phase with MITRE technique mapping.
Describe an attack in plain language and generate a valid campaign, from entry point to impact, ready to run against a sector.
IEC 62443-aligned hardening tasks with real verification: segment the network, authenticate DNP3, deploy OPC-UA certificates, and prove each control works.
04 · TRAIN & RUN COHORTS
Instructors build timed, team-scoped exercises against a private plant per team, launch attacks at individual teams or all at once, and score detection, response and hardening live on a shared board.
Organisations, teams and users with role-based access. Each team gets its own isolated plant, so an attack on one never touches another.
Detection, response and hardening points per team and per analyst, ranked in real time. Scoring runs only while the exercise is live.
Self-paced paths, a trainee handbook and labs that complete from real console actions, so learners build muscle memory on the live range.
05 · SECTORS
Modelled on Indian critical infrastructure.
CHAKRAVYUH runs fully on-premise and air-gapped. Talk to us about exercises, cohorts and deployment.