Sanraksha.SANJAY · SOC · SIEM · SOAR TRAINING SIMULATOR

The SOC is off shift. The attackers never are.

Sanraksha.SANJAY is a complete SOC in a box: a live SIEM alert queue, SOAR playbooks and an attackable enterprise estate for training analysts on real attacks, fully offline.

Sanraksha.SANJAY console screenshot
60+correlation rules
25+attack scenarios
750+auto-graded questions
20+guided labs
10+certification tracks
0internet required

01 · DETECT

Work a real alert queue, not a slideshow.

Live telemetry from firewall, DNS, proxy, EDR, identity and OT sources is correlated into alerts with severity, SLA timers and a kill chain that maps every stage to MITRE ATT&CK.

Sanraksha.SANJAY: SIEM alert queue
SIEM · 60+ RULES

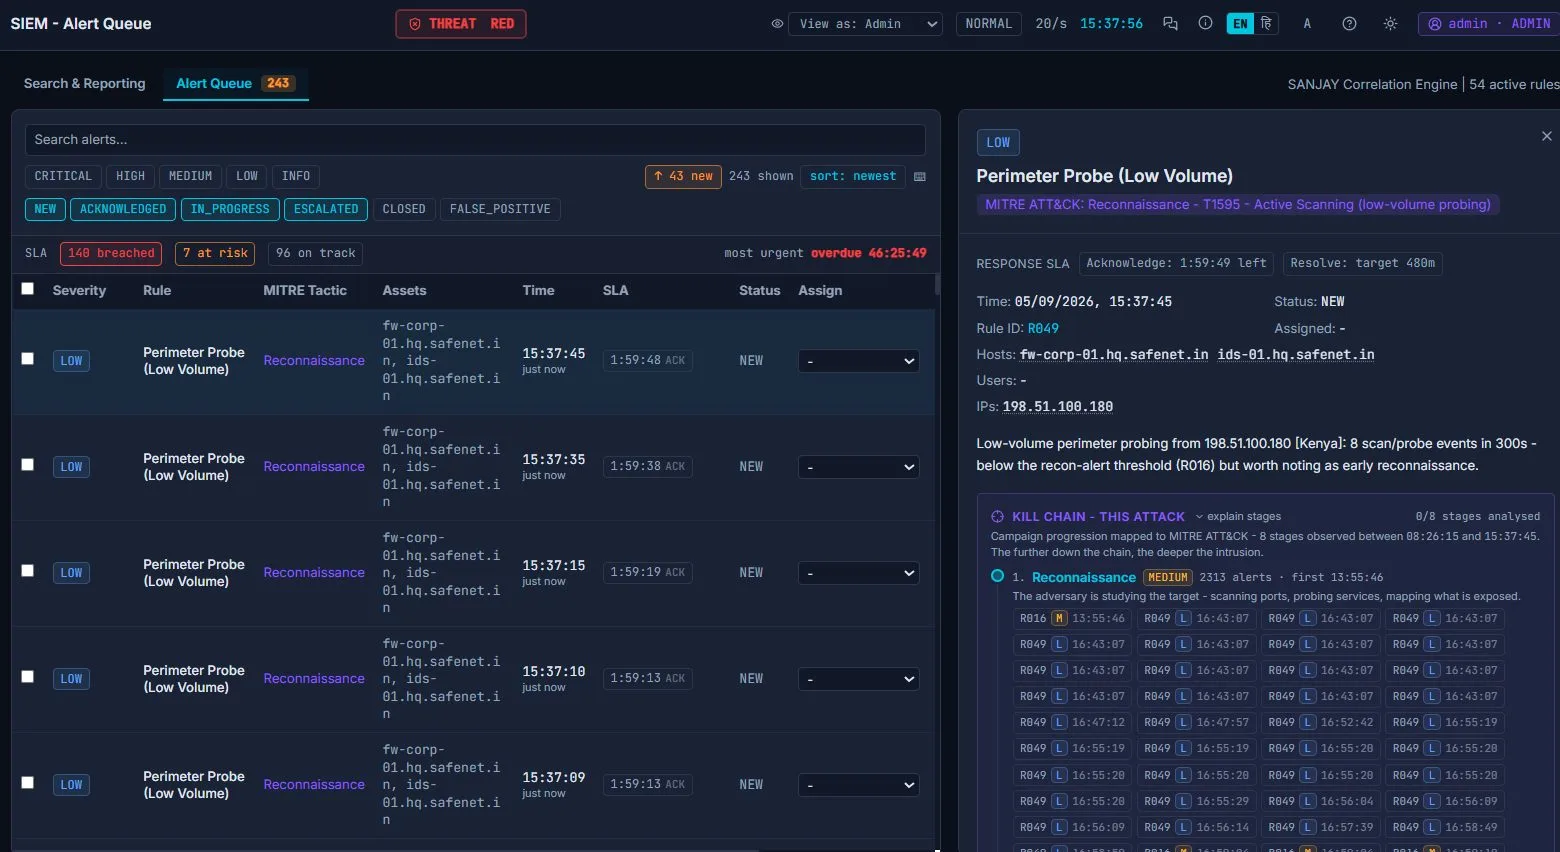
SIEM alert queue

Filter by severity and status, watch SLA countdowns turn red, and open any alert to see hosts, IPs, the rule that fired and the full kill chain of the campaign it belongs to.
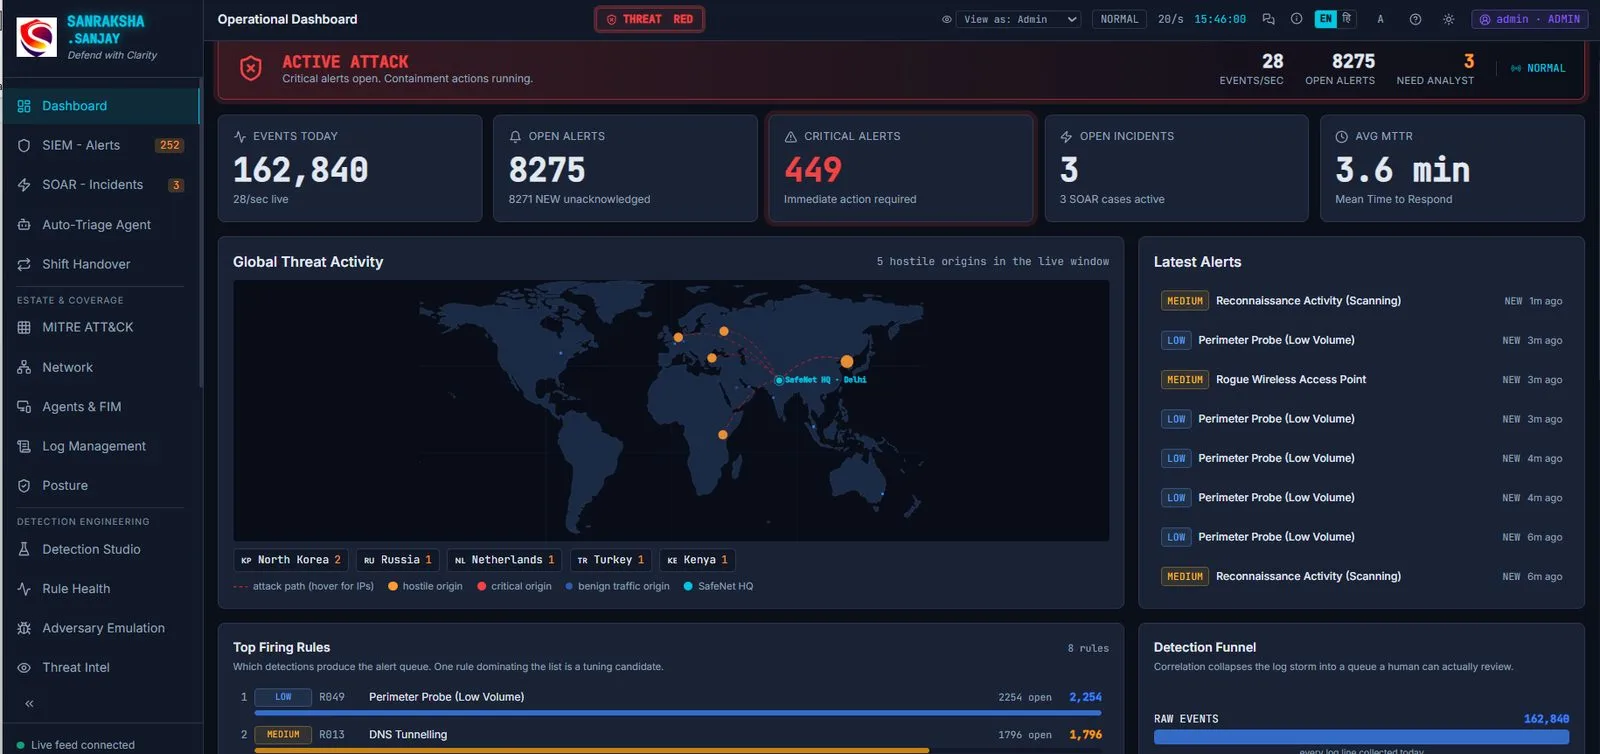
Sanraksha.SANJAY: Situational awareness
DASHBOARD

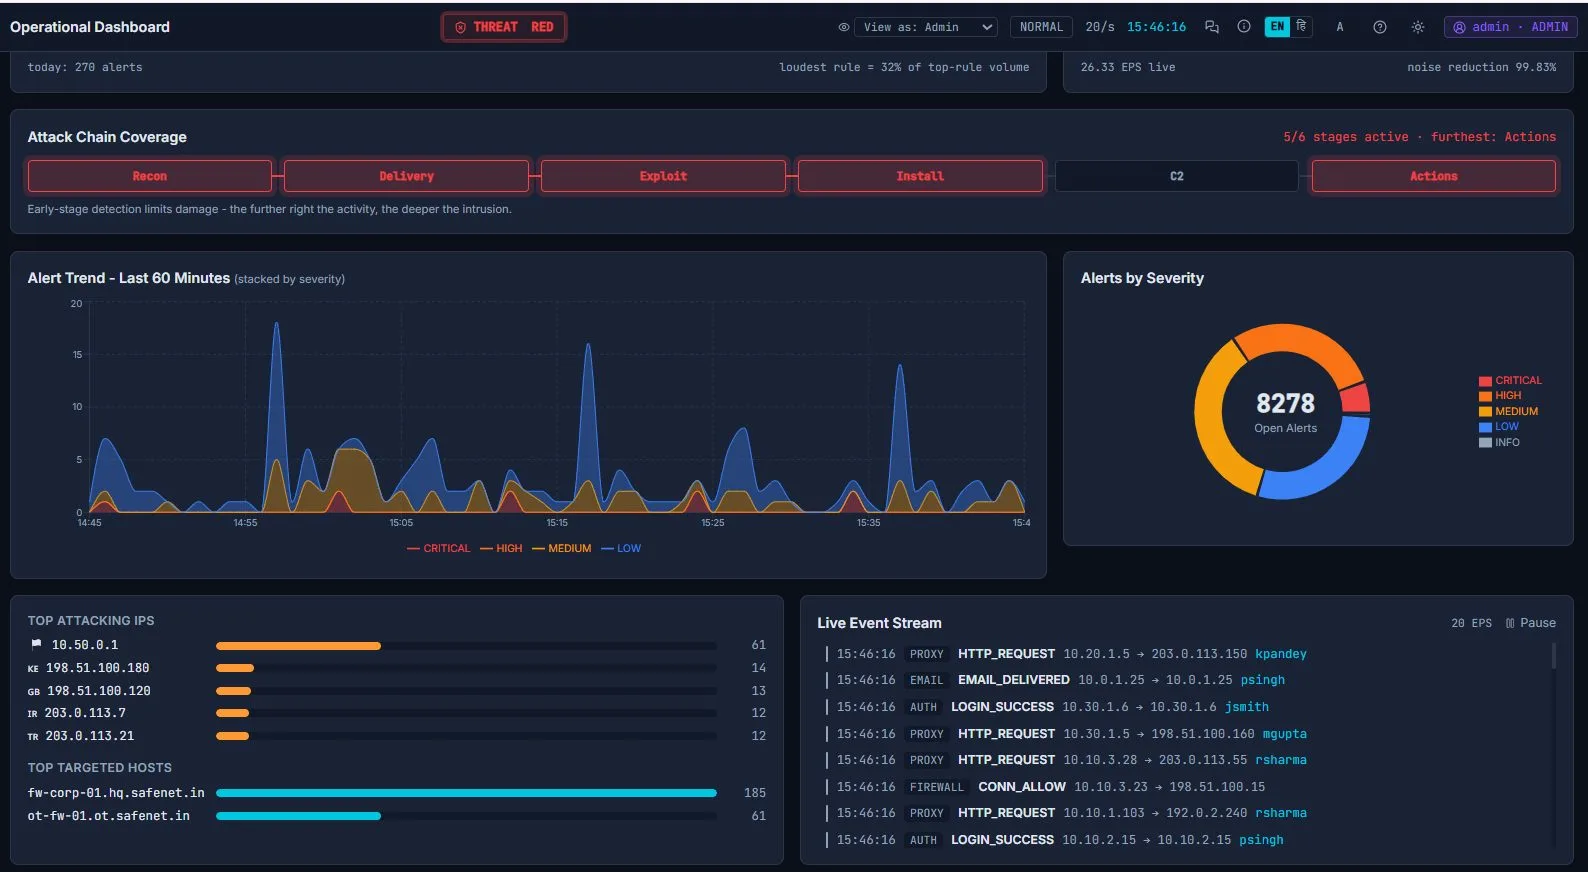
Situational awareness

Attack-chain coverage shows how deep the intrusion has progressed. Alert trend, severity mix, top attacking IPs and targeted hosts update live against a 20-events-per-second stream.

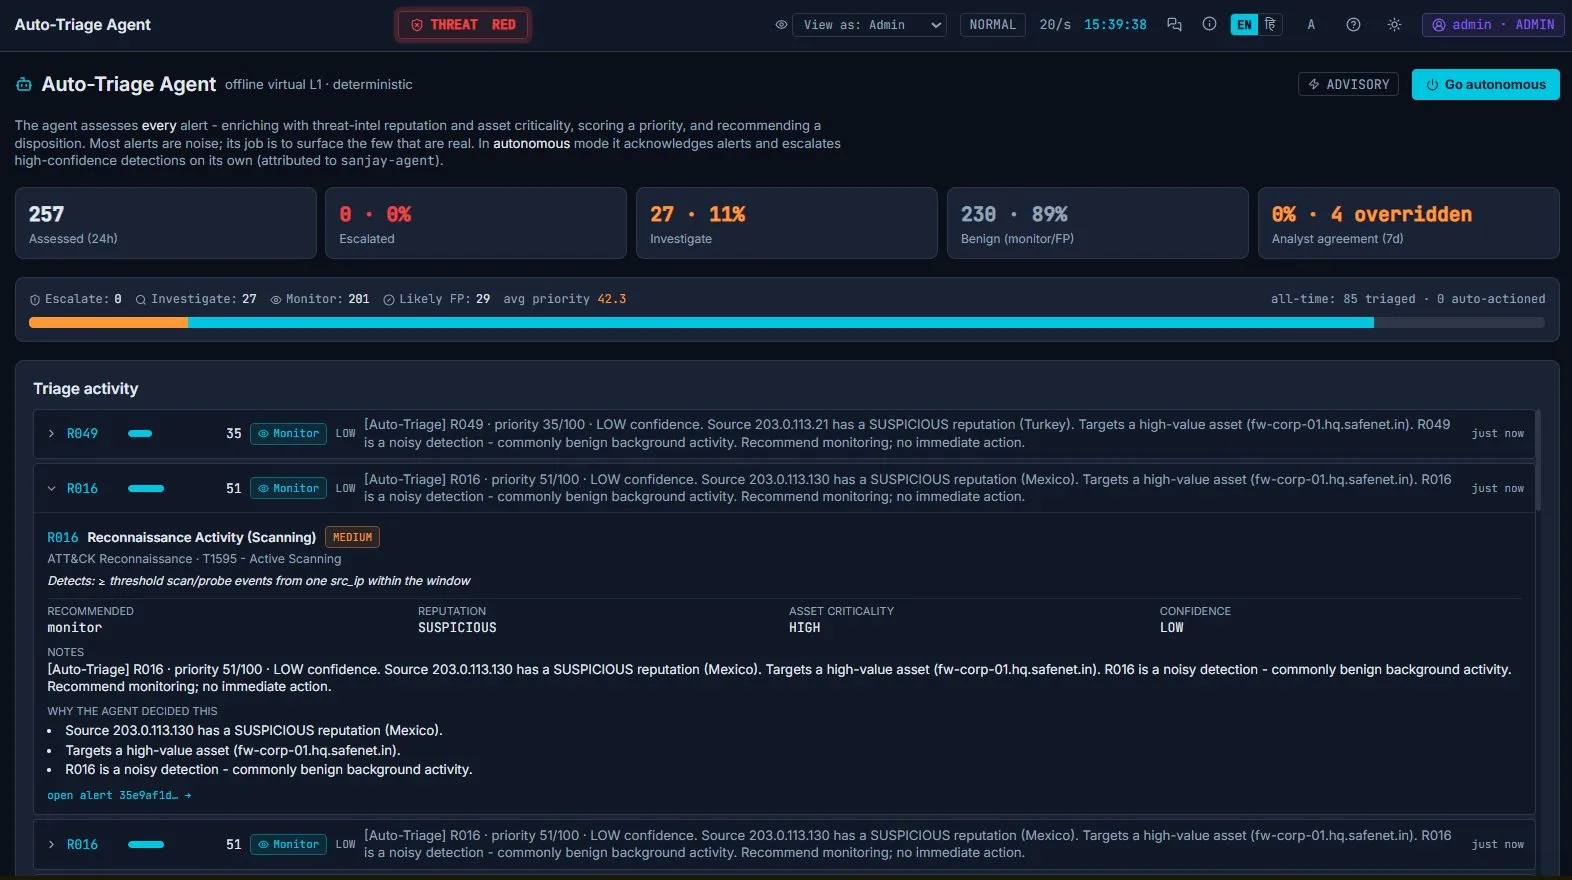
Sanraksha.SANJAY: Auto-Triage Agent
OFFLINE VIRTUAL L1

Auto-Triage Agent

A deterministic, fully offline virtual L1 scores every alert on reputation, asset criticality and confidence, explains its decision, and can acknowledge noise autonomously.

02 · RESPOND

Run the playbook. Make the containment call.

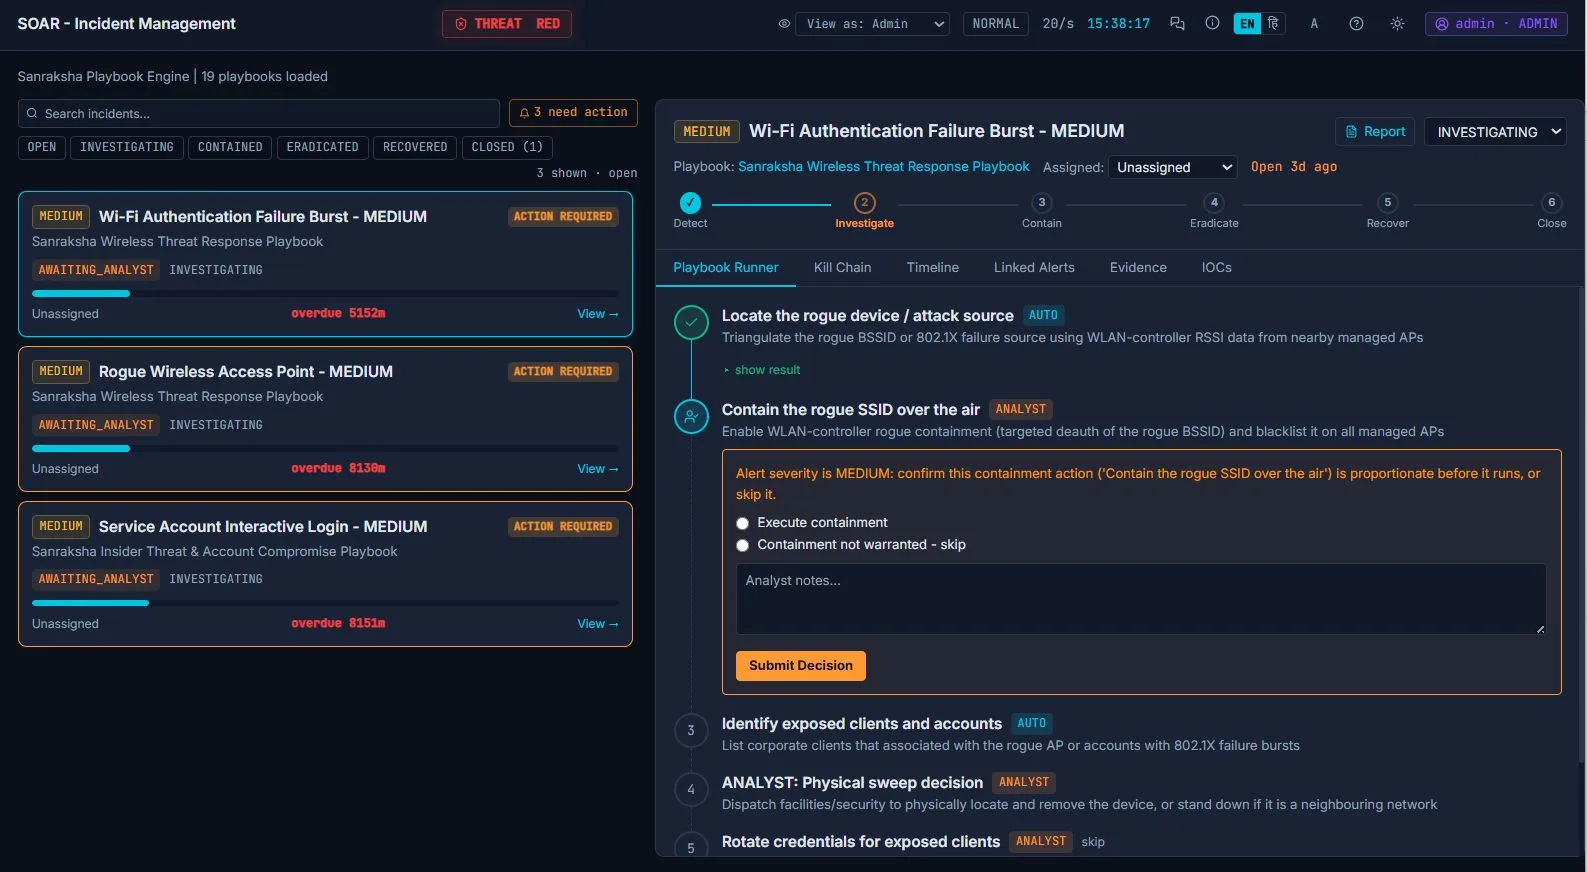
Incidents move through Detect, Investigate, Contain, Eradicate, Recover and Close. Automated steps run themselves; analyst steps wait for a human decision, and every decision is recorded.

Sanraksha.SANJAY: Analyst decision point
SOAR · 19 PLAYBOOKS

Analyst decision point

The playbook pauses before a proportionate but disruptive action and asks the analyst to execute or skip, with notes.

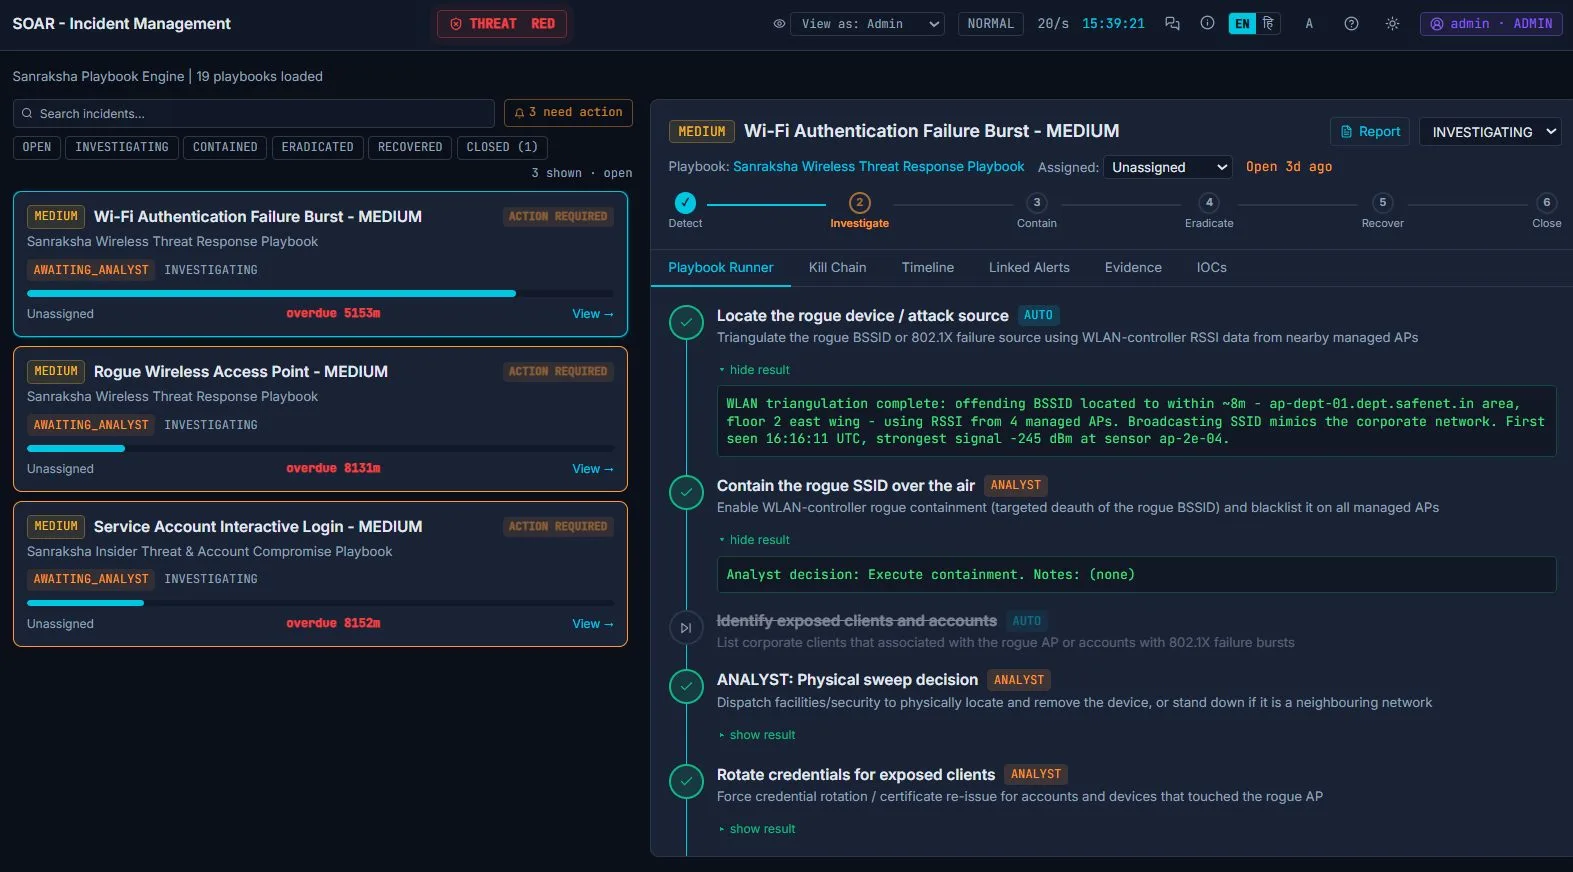
Sanraksha.SANJAY: Playbook runner
SOAR

Playbook runner

Completed steps show their evidence: WLAN triangulation results, containment executed, credentials rotated, sweep dispatched.

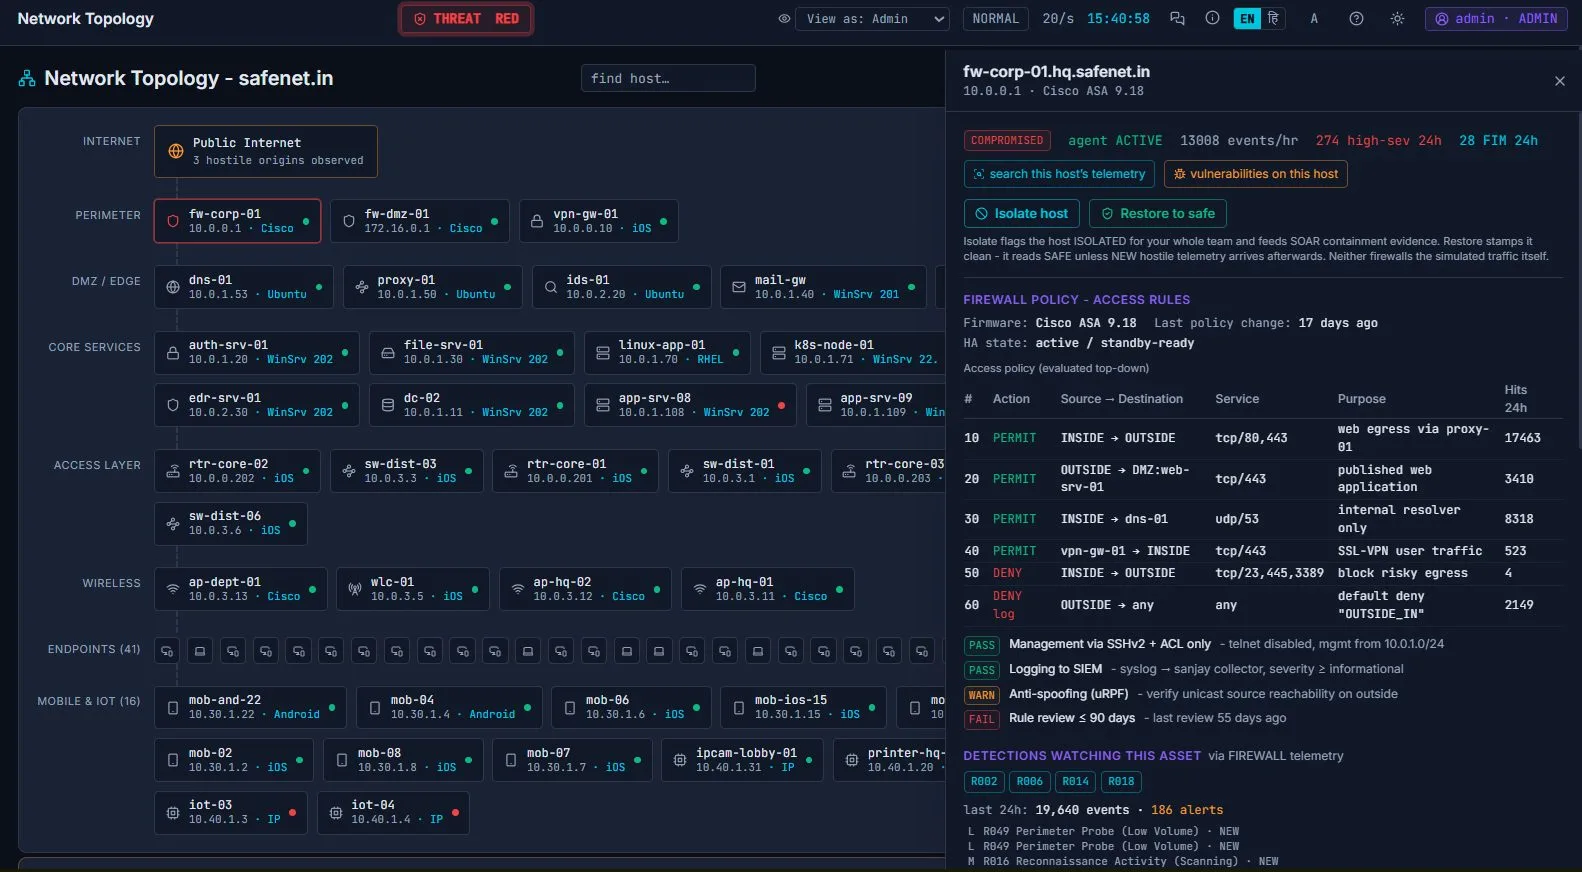
Sanraksha.SANJAY: Attackable estate
NETWORK · 121 AGENTS

Attackable estate

A whole enterprise by tier, from perimeter to OT/ICS. Inspect any host’s agent status, firewall policy and detections, and isolate or restore it with one click.

03 · HUNT & ENGINEER

Write the detections. Prove they fire.

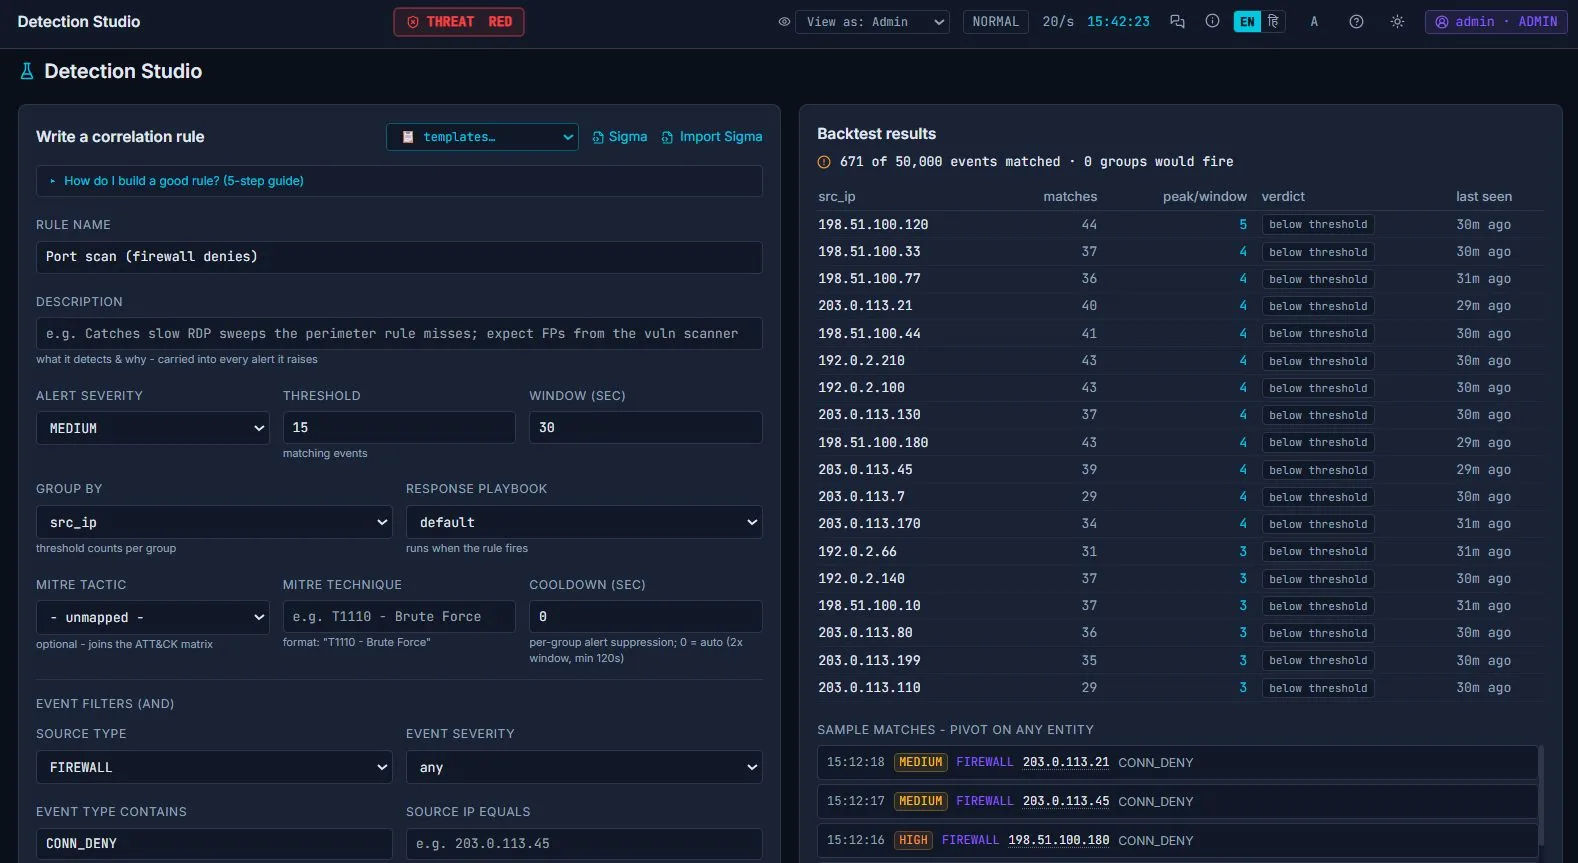
Author correlation rules, back-test them against 50,000 events, fire single ATT&CK techniques on demand to validate coverage, and hunt for the adversaries no rule has flagged.

Sanraksha.SANJAY: Detection Studio
DETECTION ENGINEERING · SIGMA

Detection Studio

Threshold, window, group-by, MITRE mapping and event filters, with an instant back-test showing which sources would have fired. Import Sigma rules or start from templates.

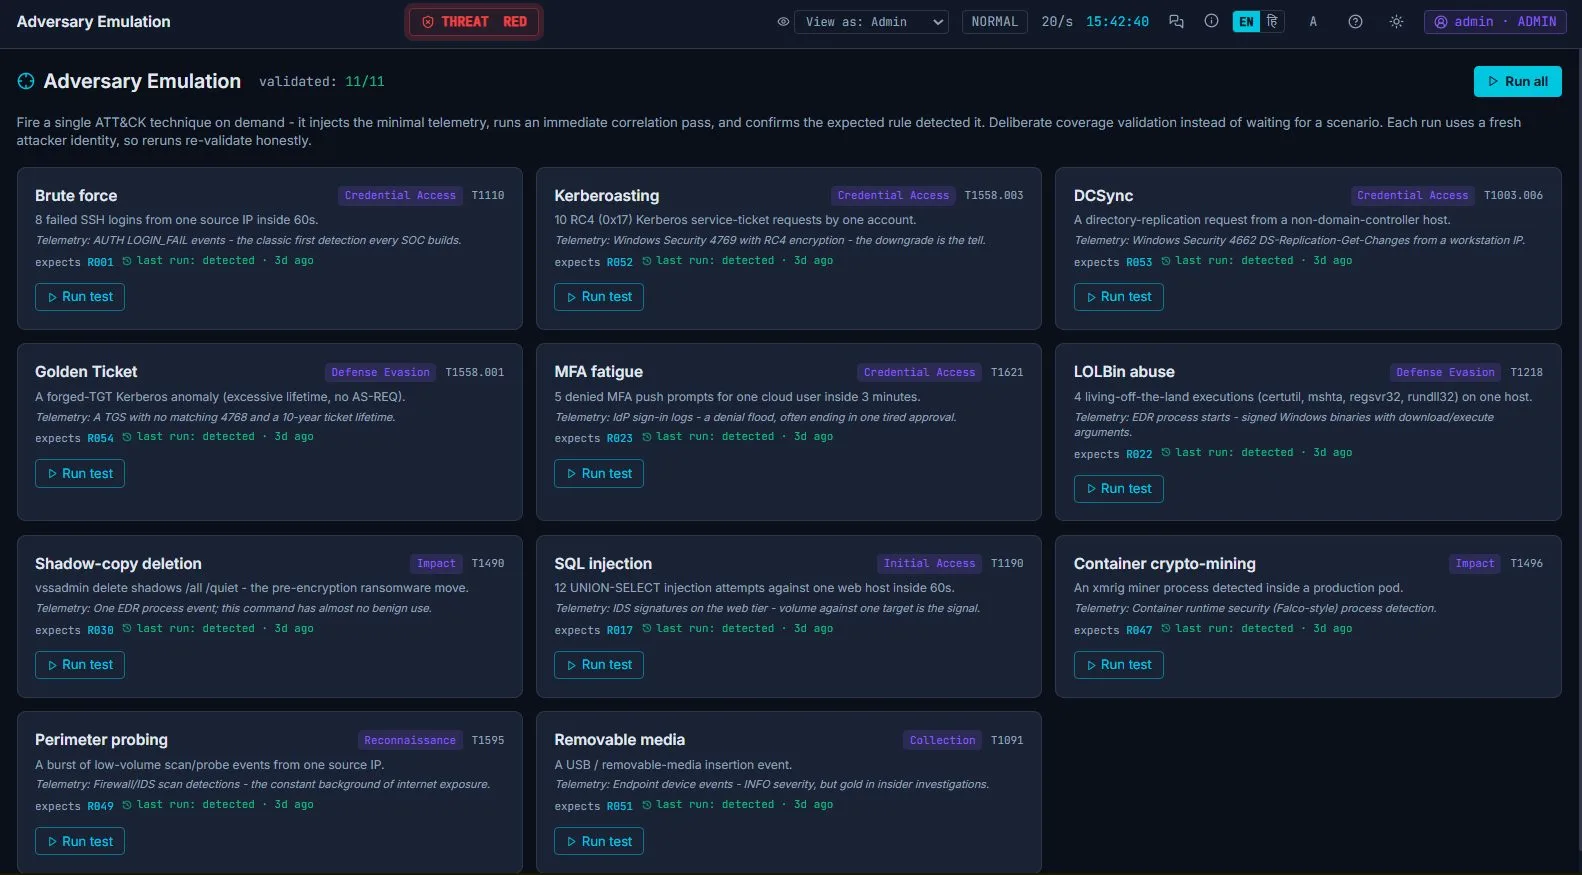
Sanraksha.SANJAY: Adversary Emulation
11 ATOMIC TESTS

Adversary Emulation

Fire Kerberoasting, DCSync, MFA fatigue, LOLBins or shadow-copy deletion on demand and confirm the expected rule caught it.

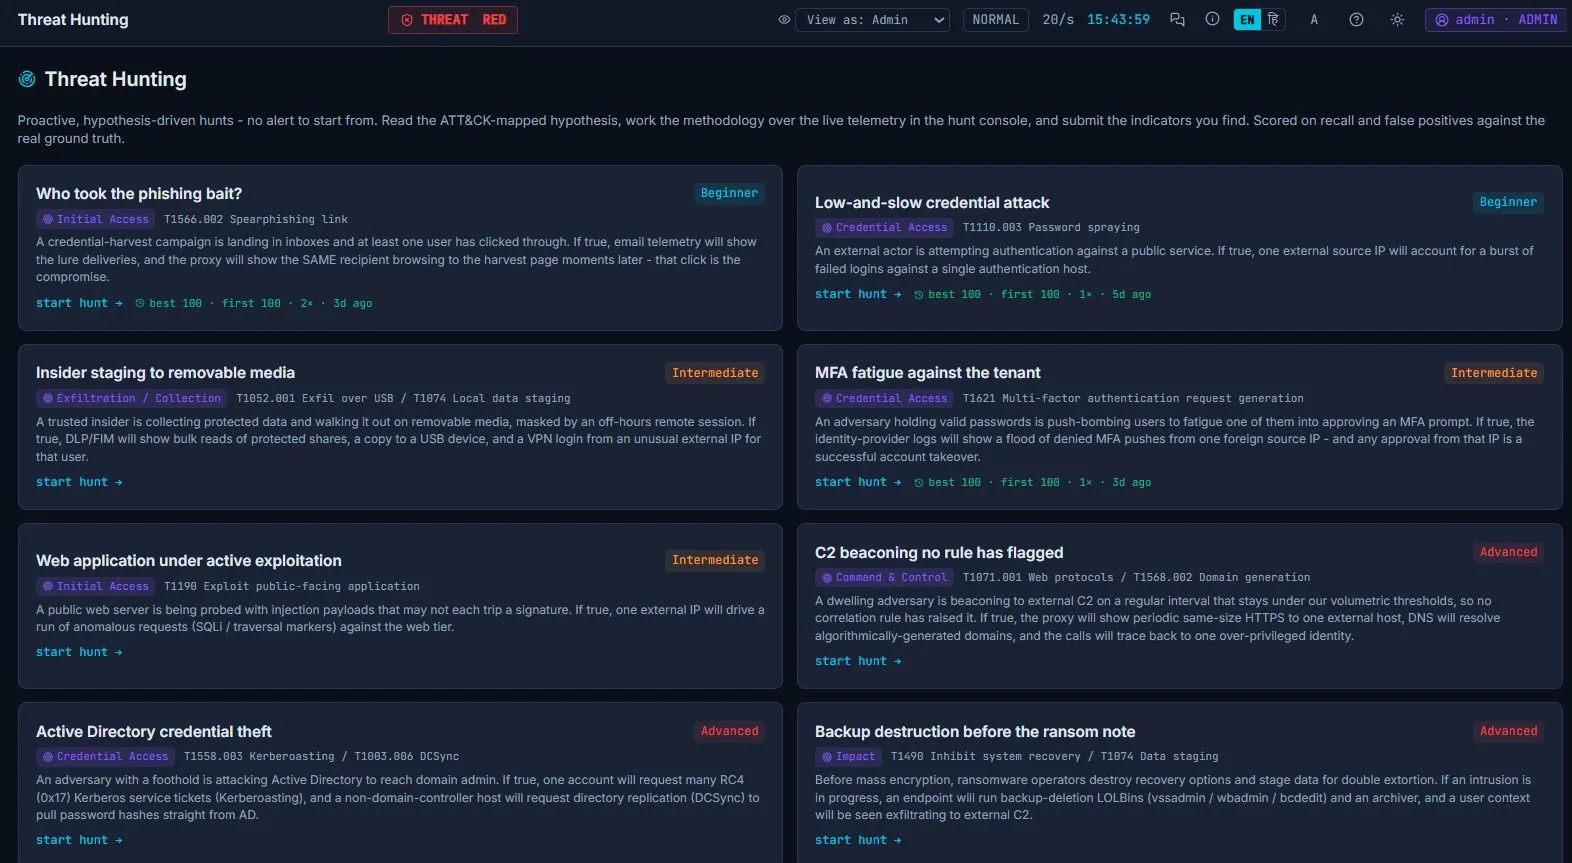
Sanraksha.SANJAY: Threat Hunting
9 HUNTS

Threat Hunting

Hypothesis-driven hunts across live telemetry, scored on recall and false positives against the real ground truth.

04 · TRAIN & RUN COHORTS

From first shift to running the whole room.

Self-paced learners follow paths and labs that complete from real console actions. Instructors build timed exercises, assign teams and drive 25+ attack scenarios against a private estate per exercise.

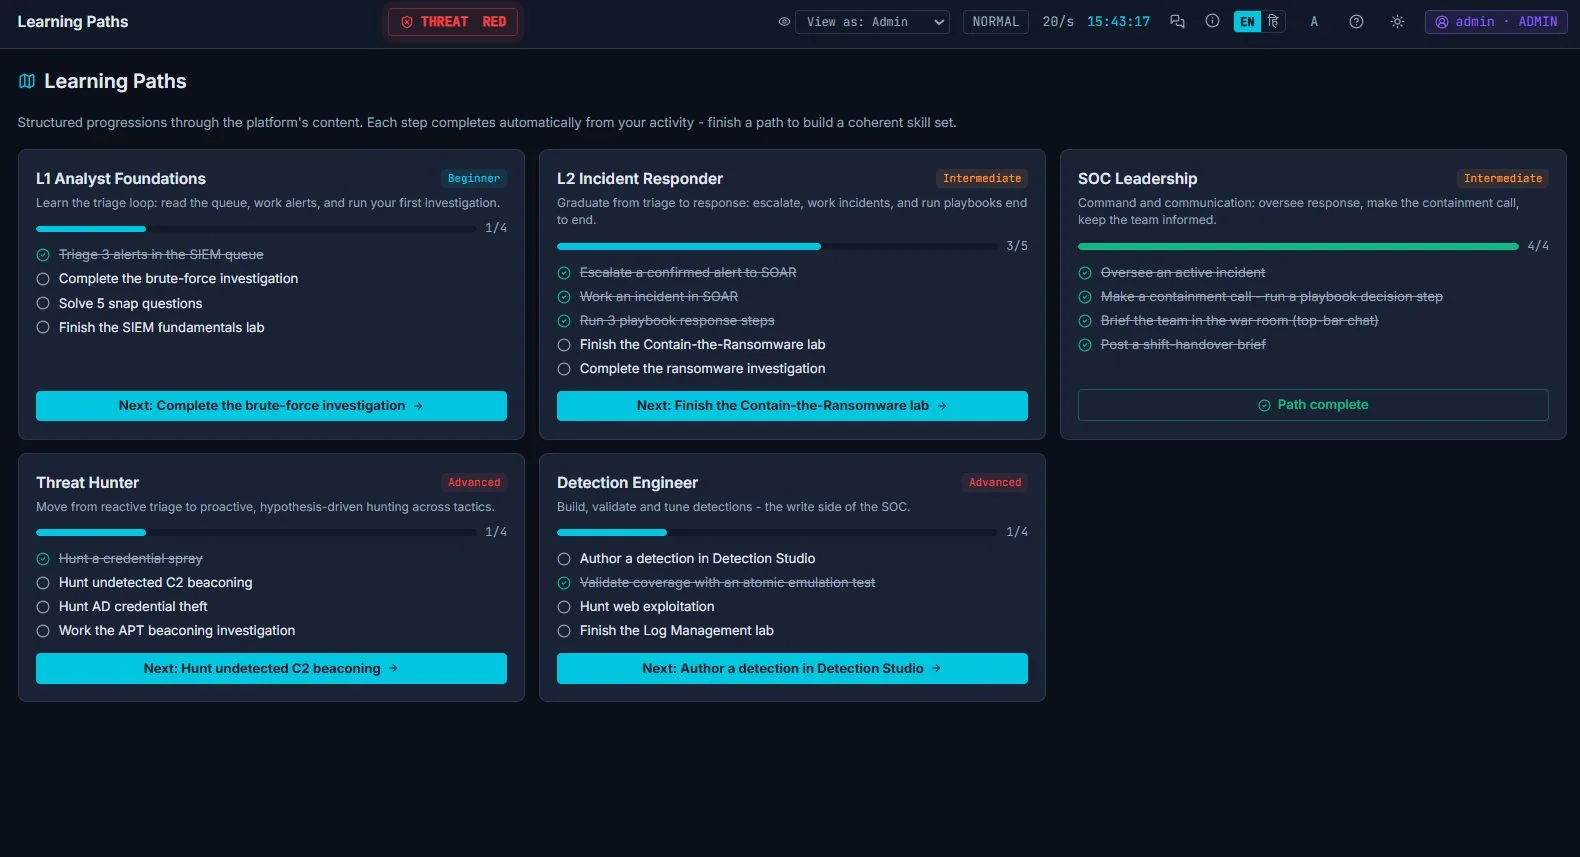
Sanraksha.SANJAY: Learning Paths
5 PATHS

Learning Paths

L1 Analyst Foundations, L2 Incident Responder, SOC Leadership, Threat Hunter and Detection Engineer. Steps tick off automatically.

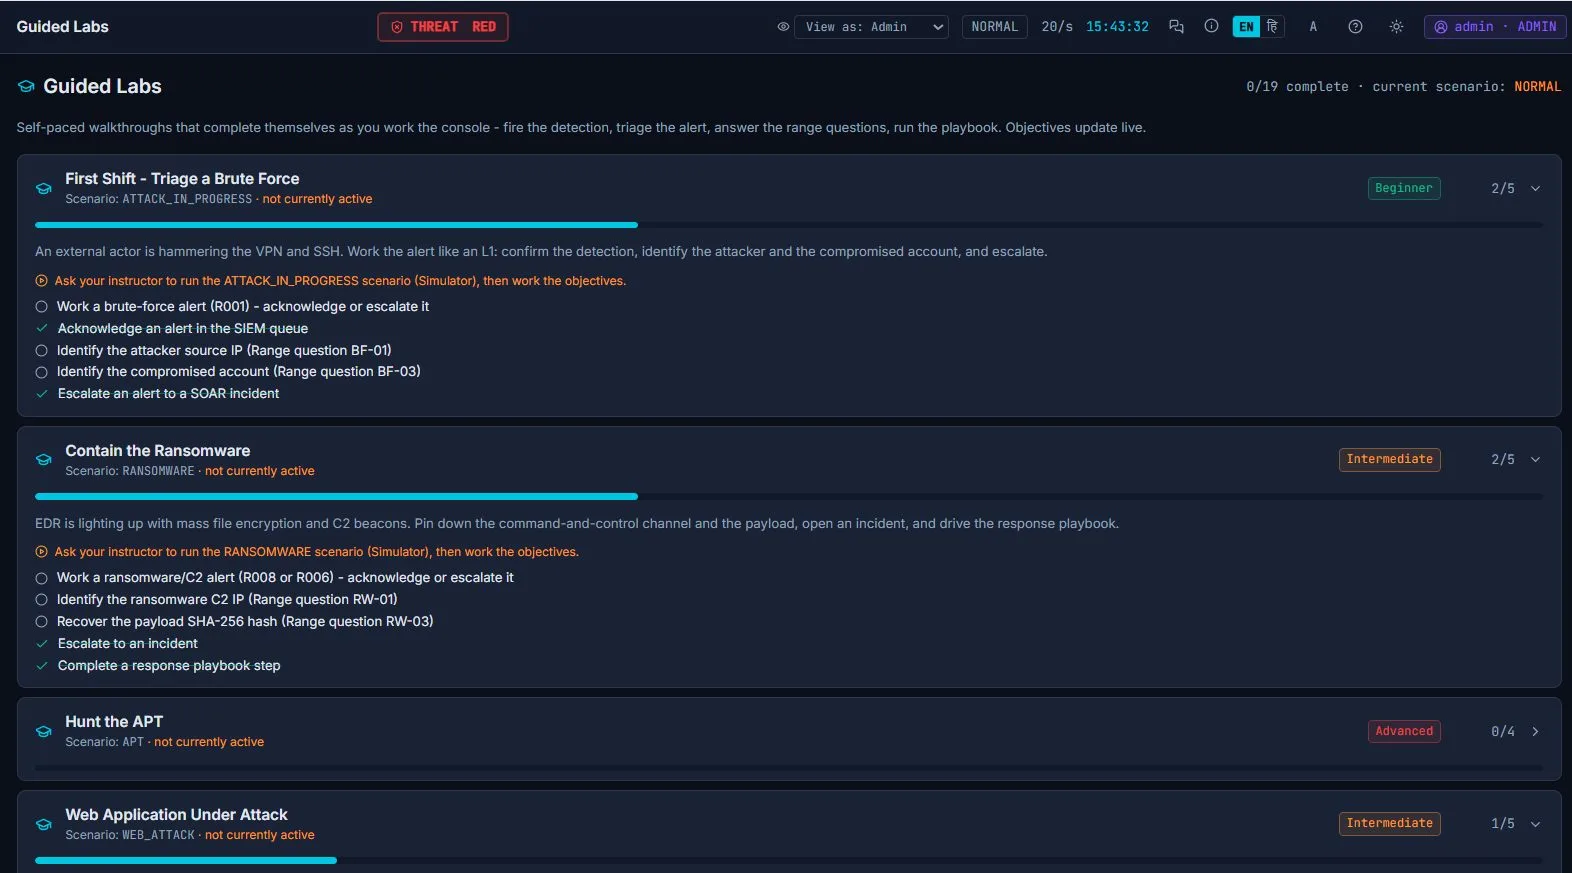
Sanraksha.SANJAY: Guided Labs
20+ LABS

Guided Labs

Beginner to Expert missions such as Triage a Brute Force or Contain the Ransomware, with objectives that update live as you work.

Sanraksha.SANJAY: Instructor console
CONTROLLER

Instructor console

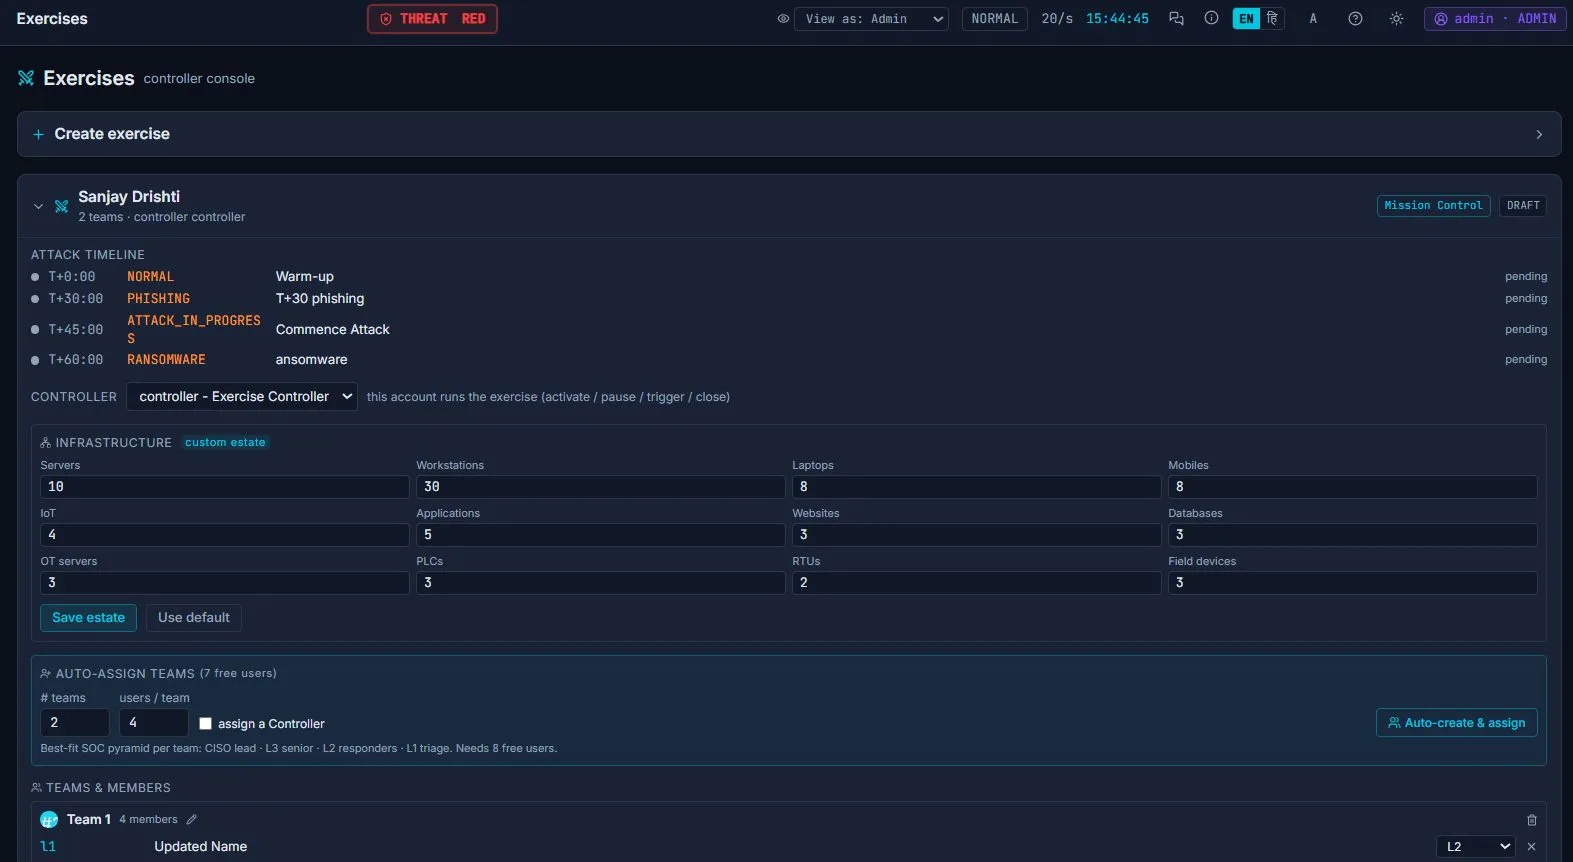
Build an exercise: attack timeline, custom estate size and auto-assigned SOC teams with L1, L2, L3 and CISO roles, then activate, pause, trigger and close.

Sanraksha.SANJAY: 25+ attack scenarios
SIMULATOR

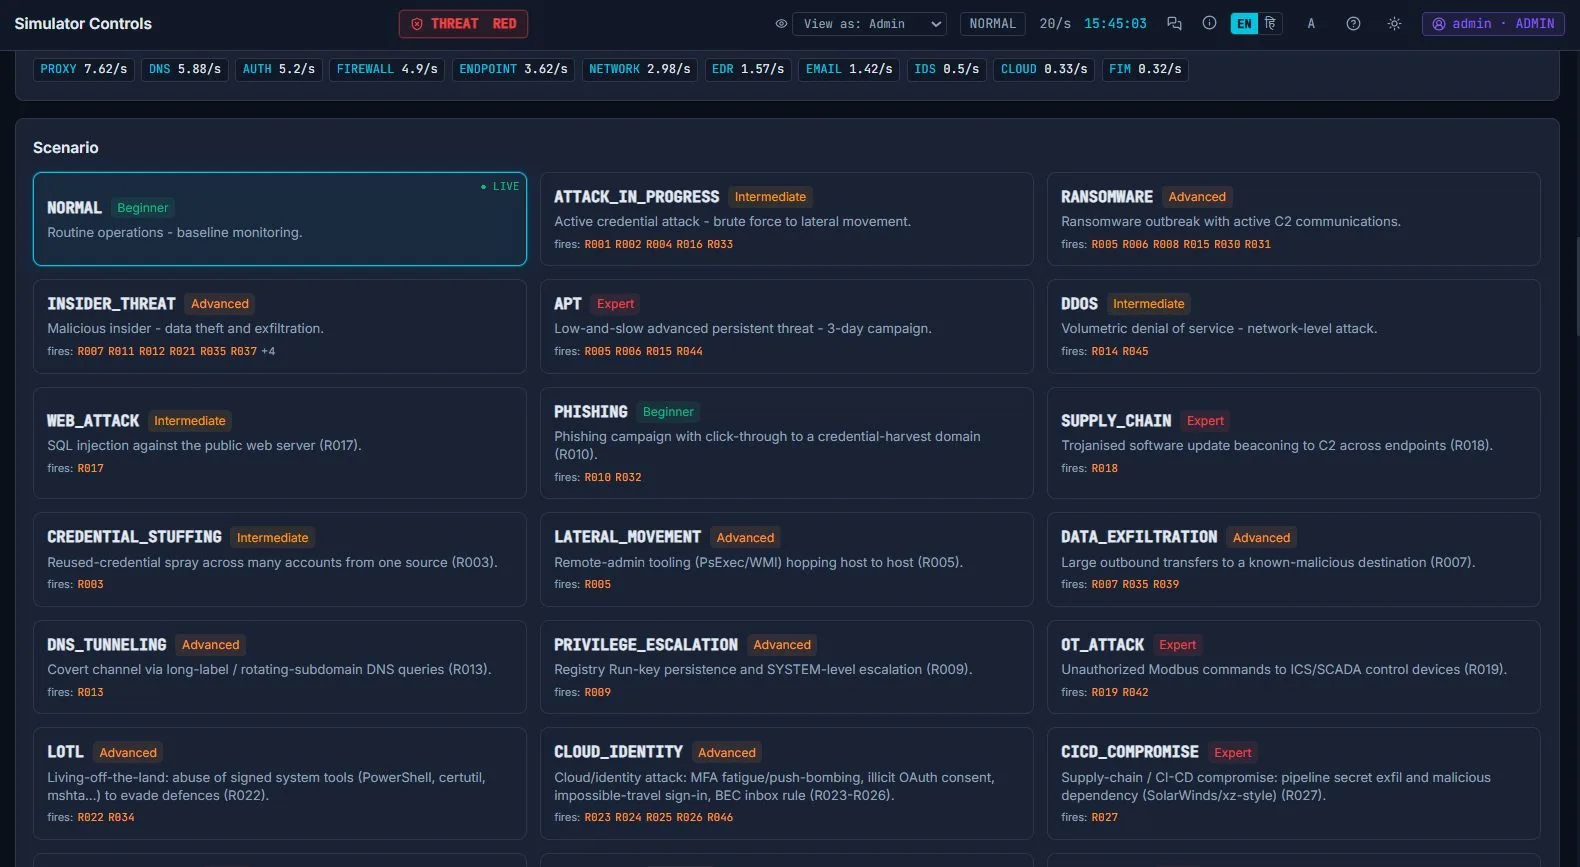
25+ attack scenarios

Phishing to APT, insider threat, DDoS, DNS tunnelling, cloud identity, OT/ICS and CI/CD compromise, each tagged with the rules it exercises.

Bring your SOC team onto the range.

Arrange a demonstration, an extended training window, or a private instance for your team.